Precious
Enumeration
- Ports found
HTTP server
Danger
To make the website work I had to add the IP into hosts file
echo "10.129.80.85 precious.htb" >> /etc/hosts
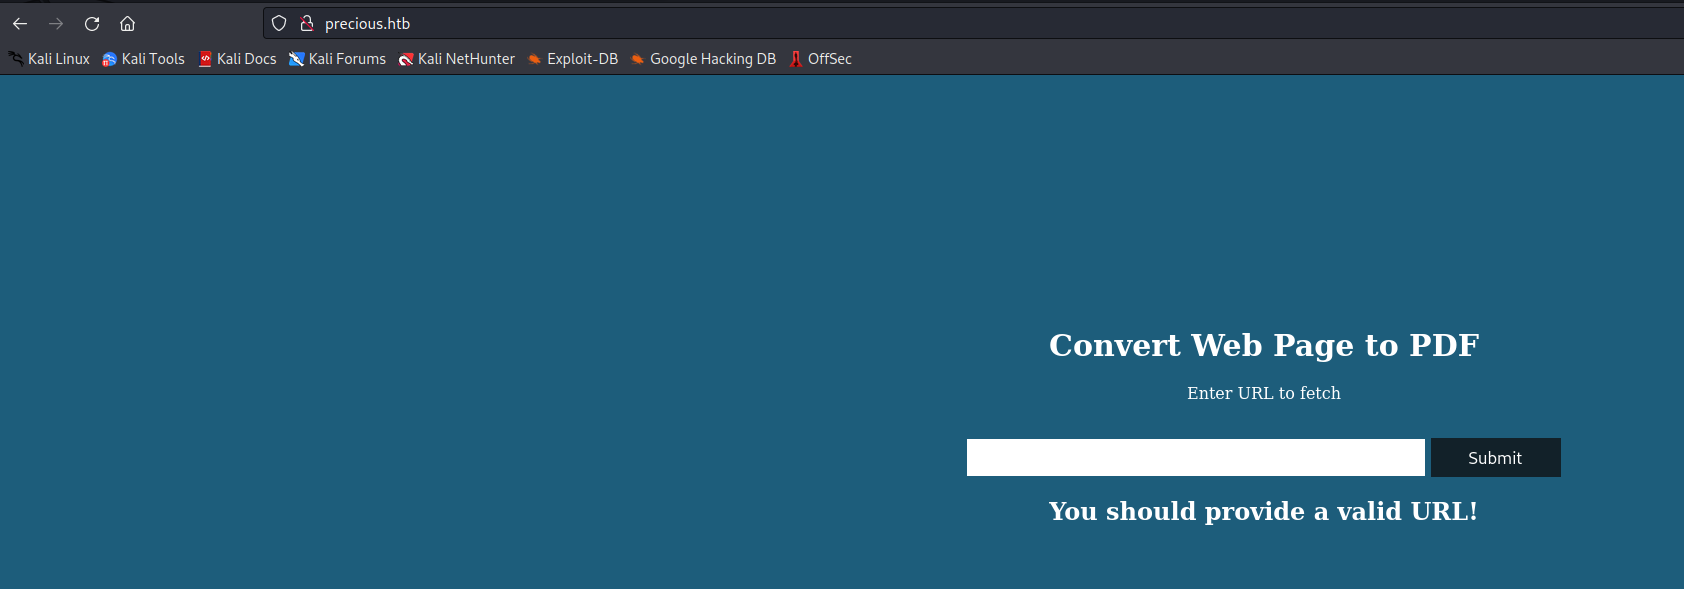
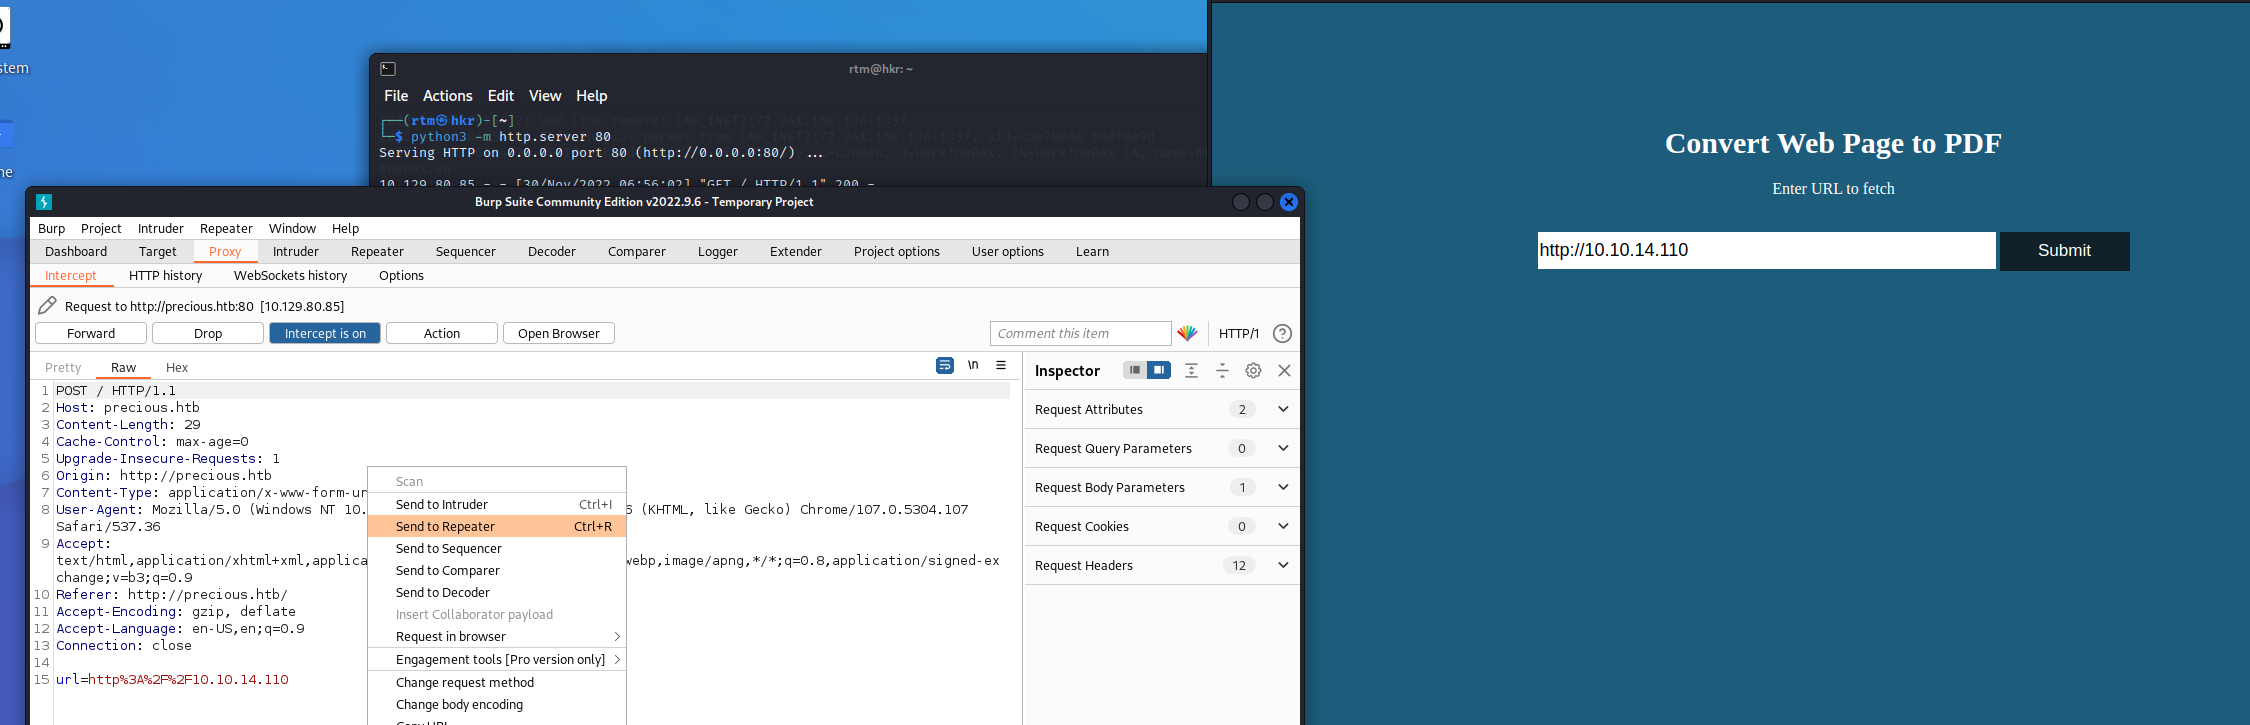
- Launch a self-hosted web server in the attacker machine to intercept and intercept the request with burp
Intercept traffic and send to repeater
With the repeater option we can identify interesting things in the response
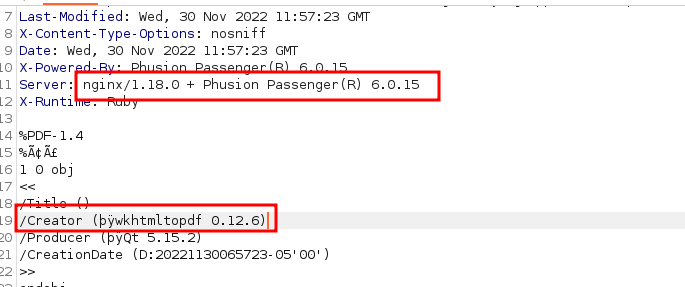
The most prominent is related to WKHTMLTOPDF, and with a quick google we can find several exploits to it, however, none of them worked.
Other possible vulnerable services
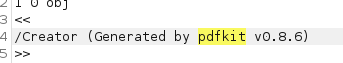
Danger
TO BE CONTINUED ....